SOFTWARE WEB APPLICATION FIREWALL
Inside the web server security works DeepFinder
Install and apply protection without stopping the service. DeepFinder protects every live web service in real time while keeping the existing request path intact.
No bypass, no gaps—continuous protection from inside the web service, without downtime.
GET /home
HTTP/1.1
GET /search?q=<script>
HTTP/1.1200 OK
HTTP/1.1 403 FORBIDDEN
HTTP/1.1GET /home?id=1024 GET /search?q=<script> Product
Keep the network. Move security closer to the application.
DeepFinder uses the traffic already decrypted by the web server, reducing the burden of a separate decryption zone and WAF certificate management. It can be deployed across on-premises, cloud, and container environments without extensively changing the existing traffic path.
Filter-based inspection
Inspect requests, responses, and uploads close to the application execution point.
Central management
Distribute policies and collect events, status, and reports through Manager.
Flexible deployment
Use one operating model across on-premises, public, private, and hybrid clouds.
How DeepFinder works
Protection happens close to the application
Each web server performs distributed inspection while Manager keeps policies, events, and operating status consistent.
Client request
Normal web and API traffic reaches the existing web service path.
Web server + Filter
The Filter inspects decrypted requests and responses inside the web server and applies detection or blocking policies.
Central Manager
Manager distributes policies and consolidates events, server status, and reports from distributed Agents.
Deploy close to the application while keeping the existing traffic path.
Inspect the data already decrypted by the web server.
Manage heterogeneous web servers and cloud environments in one place.
Certifications
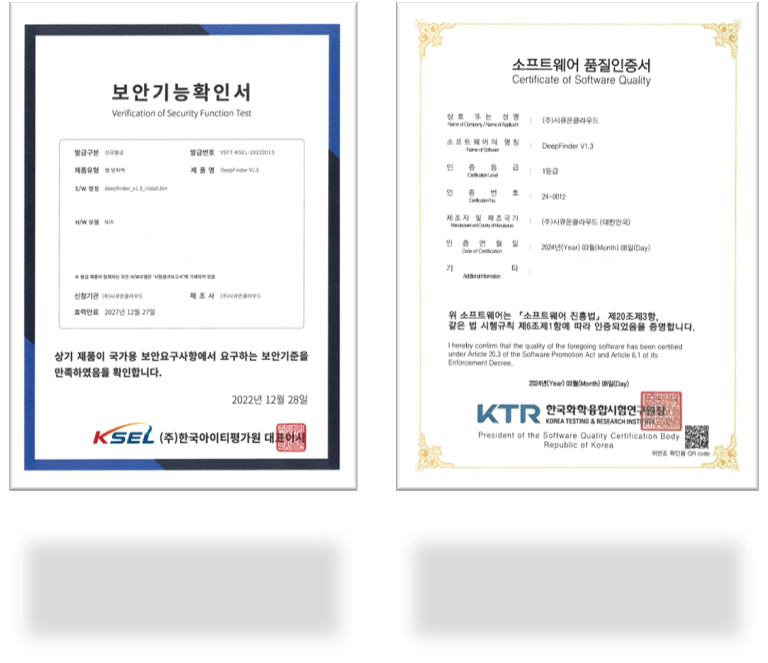
Product trust verified through Security Function Verification and GS Certification
DeepFinder V1.3 meets Server Common Security Requirements V3.0 R1 and Web Firewall Security Requirements V3.0 R1. Of 58 total requirements, it satisfies all 45 mandatory items; 11 items are not applicable, and 2 optional items are not provided.
All 45 mandatory security requirements are satisfied.
Features
Protection beyond attack signatures
DeepFinder combines web attack defense with file protection, granular policy control, and centralized operations.
Web attack defense
Detect and block SQL injection, XSS, command injection, brute-force attempts, scanners, and automated attack tools.
File and data protection
Inspect upload names, extensions, and headers, detect file tampering, and identify sensitive-data or error-message exposure.
Granular policy control
Apply detect, block, or allow policies by domain, URL, method, header, parameter, cookie, and IP.
Centralized operations
Monitor logs and system status, automate reports, and integrate with SYSLOG, SIEM, and operational APIs.
Managed ASP Service
Security continues after deployment
NEOSECUNIX supports the operating cycle from initial policy design to tuning, updates, technical support, and reporting.
Deploy
Review the environment, install Agents, and configure initial policies.
Operate
Review detections and continuously tune exceptions and service-specific policies.
Update
Apply security-pattern, policy, and product-release updates.
Support
Provide technical assistance, security reports, and ongoing operational coordination.
REFERENCE
Deployment Cases
Real-world operational scenarios and the problems solved.
CASE 01 · PRIVATE CLOUD
Case 1: Private cloud and Kubernetes
- Problem
- An integrated WAF was needed across Nginx and container workloads.
- Applied
- Filter deployment on each instance + central Manager
- Result
- Unified policy and event operations across heterogeneous environments.
CASE 02 · AUTO SCALING
Case 2: Event-driven traffic surge
- Problem
- Security devices became a bottleneck at peak.
- Applied
- Agent automation aligned with Auto Scaling
- Result
- Stable service without performance degradation.
SCALE
CASE 03 · ONE VIEW
Case 3: Large-scale hosting operations
- Problem
- Installation, updates, and monitoring were fragmented across heterogeneous servers.
- Applied
- Remote Agent operations + centralized policy and logs
- Result
- Established a single operational view and standardized maintenance.
CASE 04 · HYBRID / GLOBAL
Case 4: Overseas and hybrid operations
- Problem
- Policies and management were separated across regions and infrastructure.
- Applied
- Central Manager across on-premises, cloud, and overseas sites
- Result
- Improved remote operations and policy consistency.
LET'S TALK
Tell us about your environment. We will recommend an approach based on similar deployments.
PARTNERS
Growing together.


